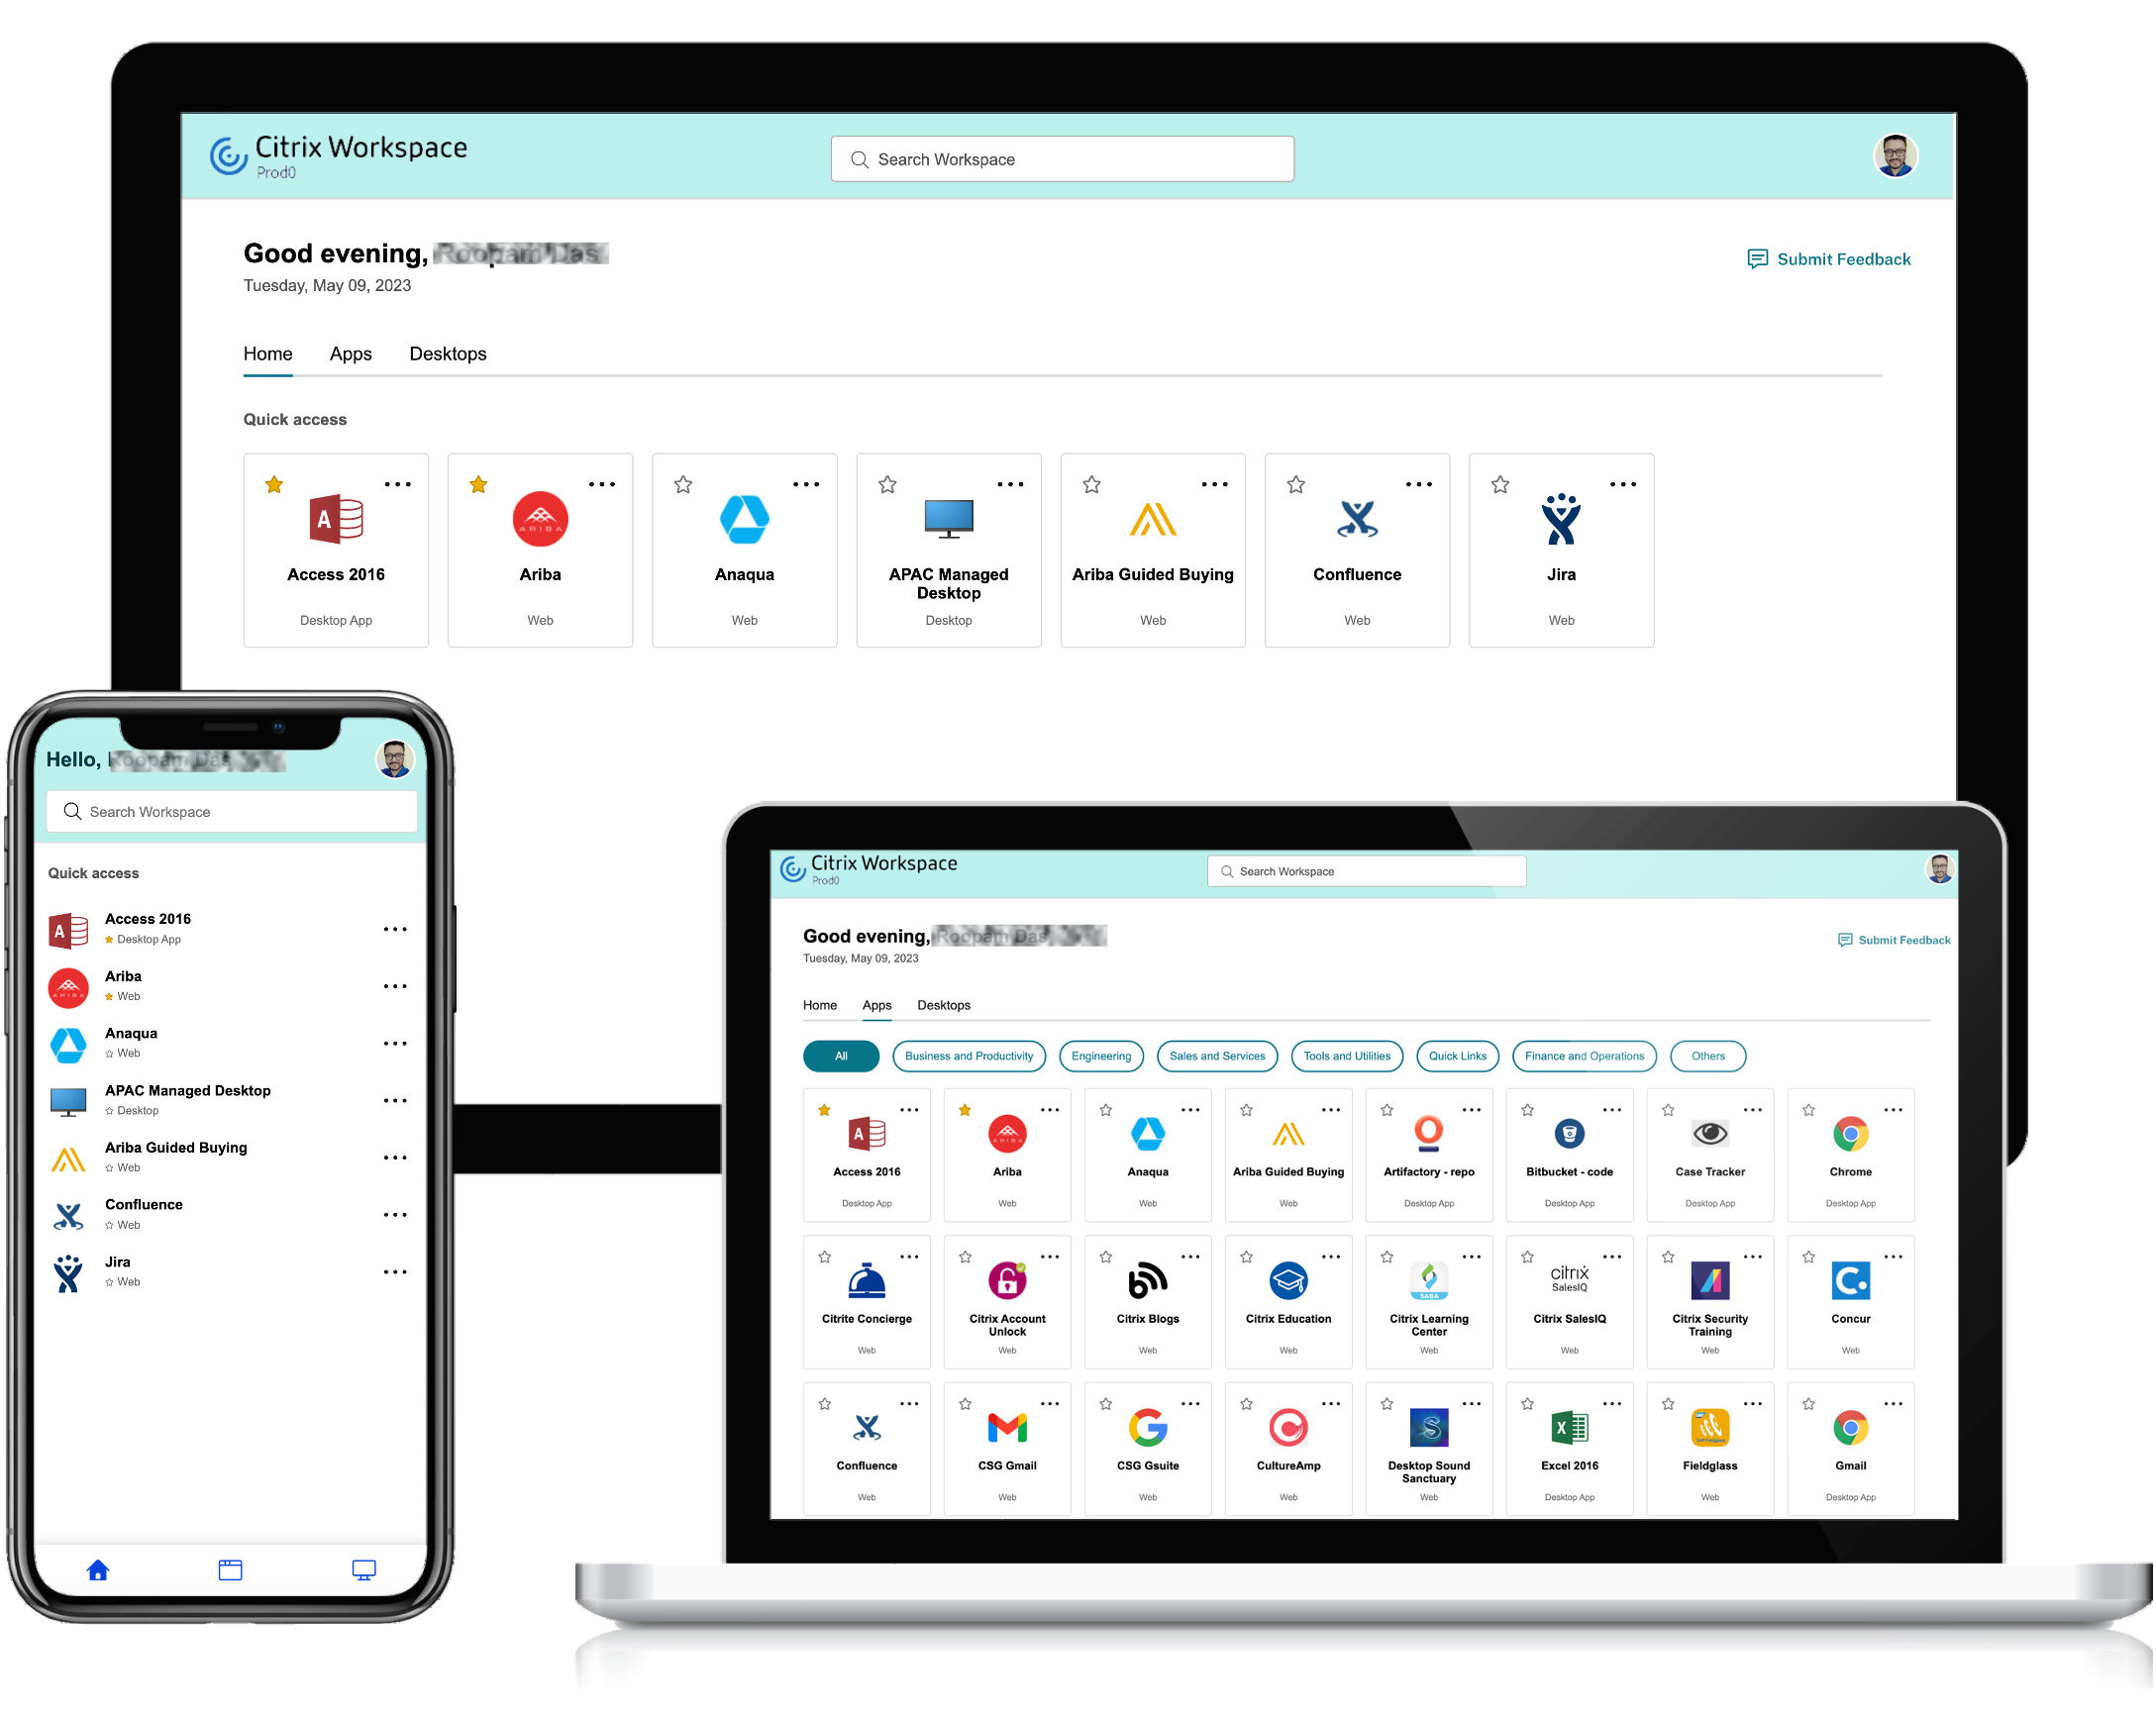
Modern organizations face immense pressure to modernize legacy systems without disrupting daily business continuity. Enterprise digital transformation relies heavily on infrastructure layers that handle massive concurrency, stringent security requirements, and distributed user access. Virtualization platforms and application delivery controllers form the backbone of these hybrid environments, ensuring that core operations scale smoothly across disparate physical locations and cloud providers.
Architecting resilient enterprise networks requires balancing user accessibility with strict data governance. As organizations migrate legacy workloads to multi-cloud setups, infrastructure teams must manage performance bottlenecks, latency variations, and security compliance. This analysis examines how enterprise virtualization and application delivery technologies support large-scale digital initiatives, common architectural hurdles, and practical strategies for optimizing hybrid environments.
Core Architectural Components of Enterprise Virtualization
Scaling enterprise operations starts with a centralized delivery model that decouples applications and desktops from local hardware. By utilizing virtual desktop infrastructure (VDI) and desktop-as-a-service (DaaS) frameworks, organizations provision resources from a single administrative plane.
- Centralized Control Layers: Core delivery controllers manage connection requests, authenticate users against directories like Microsoft Active Directory, and broker sessions between endpoints and host servers.
- Resource Provisioning: Automated machine catalogs and dynamic delivery groups allow system administrators to spin up hundreds of standardized virtual instances rapidly.
- Display Protocols: Optimized remote display protocols, such as Citrix HDX, compress graphical data and prioritize traffic packets to maintain responsiveness over constrained or high-latency wide-area networks.
When deploying these systems across multi-cloud architectures, maintaining consistent policy enforcement prevents administrative drift. Administrators configure role-based access control (RBAC) to ensure that users access only the applications and data necessary for their specific organizational roles. To see the full picture, check out the detailed article by The New York Times.
Network Optimization and Application Delivery
Behind every responsive virtual desktop lies a sophisticated traffic management layer. Enterprise environments handle thousands of simultaneous user requests, making efficient load balancing and SSL acceleration critical for performance.
Application delivery controllers (ADCs) sit at the network edge to inspect incoming traffic, terminate SSL connections, and cache static assets before requests ever hit backend servers. This offloading reduces server overhead and speeds up application response times. Furthermore, intelligent global server load balancing (GSLB) routes user traffic to the nearest available data center, ensuring high availability and disaster recovery readiness if a primary site experiences an outage.
Managing Microservices and Containerized Workloads
As organizations transition from monolithic applications to microservices, container orchestration platforms like Kubernetes introduce unique ingress networking challenges. Exposing HTTP, HTTPS, and TCP services securely across distributed clusters requires specialized container-native ingress controllers. Integrating high-performance load balancers with container ecosystems allows site reliability engineers (SREs) to monitor metrics like latency, error rates, and saturation across both legacy virtual machines and modern containerized apps.
Security Models in Distributed Enterprise Environments
Securing a perimeter-free workforce demands a multi-layered defense strategy. Traditional castle-and-moat security models fail when employees and third-party contractors connect from unmanaged devices and personal computers.
Enterprise architectures address this risk through contextual access policies and zero-trust principles. Key security mechanisms include:
- Granular Multi-Factor Authentication (MFA): Enforcing step-up authentication based on user risk profiles, device posture, and geographic anomalies.
- Endpoint Isolation: Preventing data exfiltration by blocking local file downloads, clipboard transfers, and local drive mapping on unmanaged personal devices.
- Anti-Screen Capture Policies: Applying visual security layers that render application screens blank if unauthorized capture software attempts to record sensitive sessions.
- Session Recording: Automatically capturing and archiving user sessions in highly regulated sectors like healthcare and finance to satisfy compliance mandates without third-party tools.
For further reading on building resilient architectures, explore the CISA Zero Trust Maturity Model and the NIST Cloud Computing Program for standards on secure workload migration.
Common Implementation Mistakes and How to Avoid Them
Enterprise technology migrations frequently encounter roadblocks due to poor initial planning or misconfigured resource allocations. Recognizing these pitfalls helps engineering teams protect project timelines and budgets.
- Underestimating Network Bandwidth Requirements: Deploying VDI without analyzing peak concurrent session loads leads to packet congestion and poor user experience. Always conduct thorough bandwidth profiling before rolling out graphics-heavy applications.
- Ignoring User Experience (UX) Monitoring: Relying solely on server-up metrics leaves IT blind to actual client-side latency. Implement real-time monitoring tools like Citrix Director to track active session performance, login durations, and network bottlenecks.
- Overcomplicating Image Management: Maintaining dozens of unique golden images for different departments creates a maintenance nightmare. Leverage centralized provisioning services to stream applications on-demand rather than managing bloated desktop images.
- Neglecting Disaster Recovery Testing: Assuming high-availability clusters will failover seamlessly without regular simulation tests often results in extended downtime during actual outages.
Frequently Asked Questions
What is the primary function of an application delivery controller in an enterprise network?
An application delivery controller optimizes traffic flow, balances server loads, accelerates SSL encryption, and protects web applications from common layer 7 cyber attacks before traffic reaches core backend infrastructure.
How do virtual desktop environments handle unmanaged personal devices?
Virtual desktop platforms stream the pixels of an application rather than running the code locally on the endpoint. This ensures that sensitive data remains encrypted within the corporate data center and cannot be saved or downloaded onto personal hardware.
Why is hybrid cloud deployment popular for modern enterprise virtualization?
A hybrid model allows organizations to maintain sensitive database workloads on-premises for compliance while scaling transient user desktop pools rapidly across public cloud providers during demand spikes, optimizing operational costs.
What metrics should SREs monitor in containerized ingress architectures?
Site reliability engineers should track the four golden signals: latency, traffic volume, error rates, and system saturation, alongside specific ingress throughput and backend connection health.



