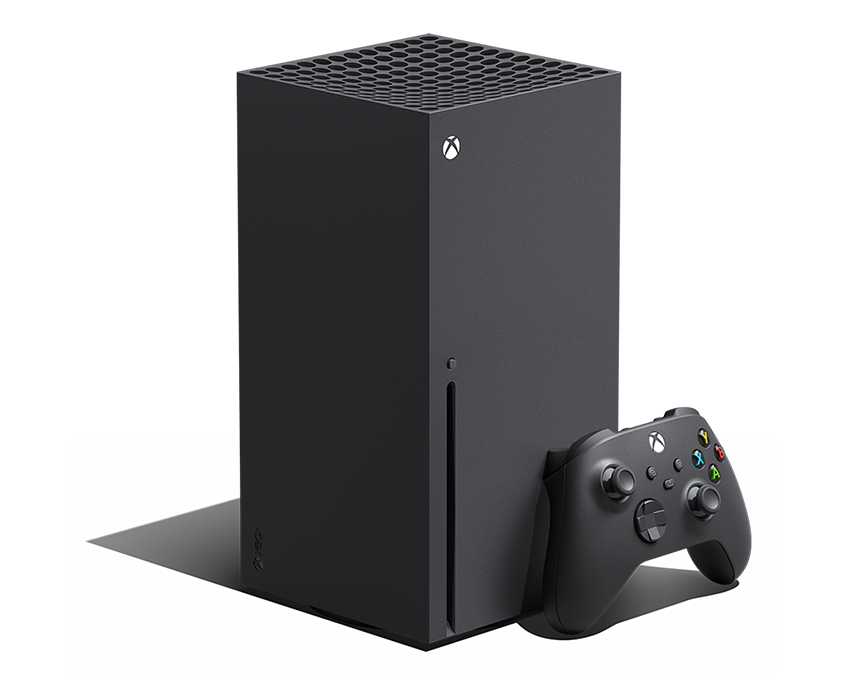
Between 2011 and 2014, an international collective of young tech enthusiasts known as the Xbox Underground managed to breach the internal networks of Microsoft, Valve, Epic Games, and even U.S. military software contractors. Operating from behind digital aliases and gamertags, these hackers siphoned unreleased source code, proprietary software development kits, and sensitive intellectual property valued at over one hundred million dollars. Unlike conventional ransomware operators seeking quick payouts, this group was driven by an obsessive curiosity for unreleased hardware and code, culminating in a sweeping federal indictment by the U.S. Department of Justice.
Understanding how a loose network of teenagers and young adults bypassed the security perimeters of one of the world's largest tech conglomerates reveals critical vulnerabilities in both digital access control and physical office security. Their operation wasn't just a digital intrusion; it combined remote exploitation with physical trespassing, forever changing how gaming corporations protect unreleased assets.
The Origins and Evolution of the Group
The collective didn't form overnight. It began as loose clusters of coders and gamers congregating on underground forums, IRC channels, and Xbox Live chat rooms. They shared a mutual fascination with reverse-engineering console firmware and dissecting early software builds. Over time, these tech enthusiasts banded together, pooling skills to form a specialized team capable of executing complex network intrusions.
By 2012, the group's focus shifted from casual modding to targeted infiltration. Members included individuals such as David Pokora from Canada, Sanadodeh Nesheiwat, Nathan Leroux, and Austin Alcala, alongside international affiliates like Dylan Wheeler operating out of Australia. Each participant brought specific proficiencies, ranging from credential harvesting and exploit development to hardware tampering and underground trade coordination.
Their primary target was Microsoft's corporate network, specifically the environments dedicated to the development of the upcoming Xbox One console and its associated software. Because game development relies heavily on remote contractors, external partner studios, and decentralized staging servers, the group exploited these peripheral access points to slip past primary firewalls.
The Anatomy of the Breach
The group's intrusion methodology relied heavily on advanced persistent threat techniques, long-term credential monitoring, and social engineering. Rather than smashing through front-facing security gates, they mapped internal directories quietly over months.
- Credential Stuffing and Phishing: The hackers targeted low-level employees and third-party contractors associated with Microsoft and partner studios like Epic Games and Valve. By capturing valid login details, they moved laterally through corporate directories without triggering standard intrusion detection alerts.
- Exploiting Development Kits: Once inside, they extracted software development kits (XDKs) for the unreleased Xbox One. These specialized units allowed them to inspect uncompiled game builds, test proprietary firmware, and understand how the console's security architecture handled encryption.
- Physical Infiltration: In an audacious escalation, some members traveled to Microsoft headquarters in Redmond, Washington. Using stolen access badges or tailgating employees, they entered physical office buildings after hours to plant hardware bugs and physically steal non-public Xbox One console prototypes.
This combination of physical theft and remote access gave them deep visibility into upcoming titles, internal communications, and proprietary operating systems.
Expanding Targets: From Video Games to Military Simulators
While gaming intellectual property was their primary currency, the group's ambitions eventually drifted into more sensitive territory. According to federal indictments filed by the U.S. Department of Justice, members successfully accessed network segments containing software related to a tactical Apache helicopter training simulator.
The breach of military-adjacent training software marked a turning point in federal law enforcement interest. What might have otherwise remained an internal corporate security matter for tech firms transformed into a high-priority national security investigation involving the Federal Bureau of Investigation (FBI). The inclusion of defense contractor data ensured that federal prosecutors would pursue the case with maximum legal gravity.
The Investigation, Arrests, and Sentencing
The walls began closing in on the collective in 2013 as federal agents coordinated international raids. Because the hackers operated across borders—spanning the United States, Canada, Australia, and Europe—the investigation required extensive cooperation between the FBI, the Royal Canadian Mounted Police, and international law enforcement agencies.
The legal fallout dismantled the group through a series of guilty pleas and historic federal sentencings:
- David Pokora: In April 2015, Pokora became the first foreign hacker ever sentenced on United States soil for intellectual property theft and computer intrusion, receiving an 18-month prison term.
- Sanadodeh Nesheiwat and Nathan Leroux: Both pled guilty to federal charges, receiving prison sentences ranging from 18 to 24 months for their roles in the conspiracy to steal proprietary Microsoft software.
- Austin Alcala: After cooperating extensively with federal authorities in subsequent cybercrime investigations, Alcala faced sentencing provisions tied to his collaboration with prosecutors.
- Dylan Wheeler: Operating from Australia and later Europe, Wheeler avoided direct U.S. extradition by relocating across international jurisdictions, though his associates faced severe legal consequences.
For a detailed look at the human and technical elements behind these investigations, independent deep-dives such as the Darknet Diaries podcast feature extensive retrospective reporting on the case.
Lessons Learned for Corporate Security
The activities of these hackers forced a massive reckoning within the technology and gaming sectors regarding how valuable intellectual property is stored and monitored. Several foundational security practices emerged directly from the vulnerabilities exposed during this era:
- Zero-Trust Network Architecture: Companies moved away from treating internal networks as inherently safe. Every access request, even from verified employee credentials, now requires continuous authentication and multi-factor verification.
- Physical-Digital Convergence: Security teams realized that physical facility access controls must integrate directly with IT monitoring. Unauthorized badge swipes or late-night building entries now trigger immediate alerts to corporate cybersecurity teams.
- Third-Party Risk Management: Because the breach originated largely through contractor and partner vulnerabilities, modern tech firms enforce strict least-privilege access policies for external vendors, limiting how deep outside developers can travel within core code repositories.
Frequently Asked Questions
What was the main goal of the hackers?
Unlike modern ransomware syndicates focused on financial extortion, the core motivation was prestige, access to unreleased technology, and the thrill of reverse-engineering proprietary gaming hardware before public release.
How much value did the stolen software represent?
Federal prosecutors estimated the total market and development value of the stolen intellectual property, source code, and hardware prototypes to be between $100 million and $200 million.
Did any members avoid prison time?
Some members who cooperated extensively with federal law enforcement received reduced sentences, probation, or entered witness cooperation agreements, while primary architects served federal prison terms.
How did the group access military software?
The group gained entry into networks connected to defense contractors through compromised credentials, demonstrating how porous corporate boundaries can inadvertently expose sensitive secondary data repositories.



