Government cybersecurity analysts and digital forensic investigators frequently face the complex task of processing large volumes of encrypted files. When dealing with intelligence operations or digital evidence, manual decryption workflows create severe operational bottlenecks. Implementing an automated batch processing pipeline for intelligence file decryption allows security teams to handle protected datasets systematically while maintaining strict regulatory compliance.
Understanding how to structure these automated decryption workflows involves examining input management, cryptographic key handling, and secure logging protocols. This guide breaks down the core architecture, implementation practices, and governance standards required to build scalable decryption pipelines without compromising data security or operational integrity.
Understanding Batch Processing in Intelligence Contexts
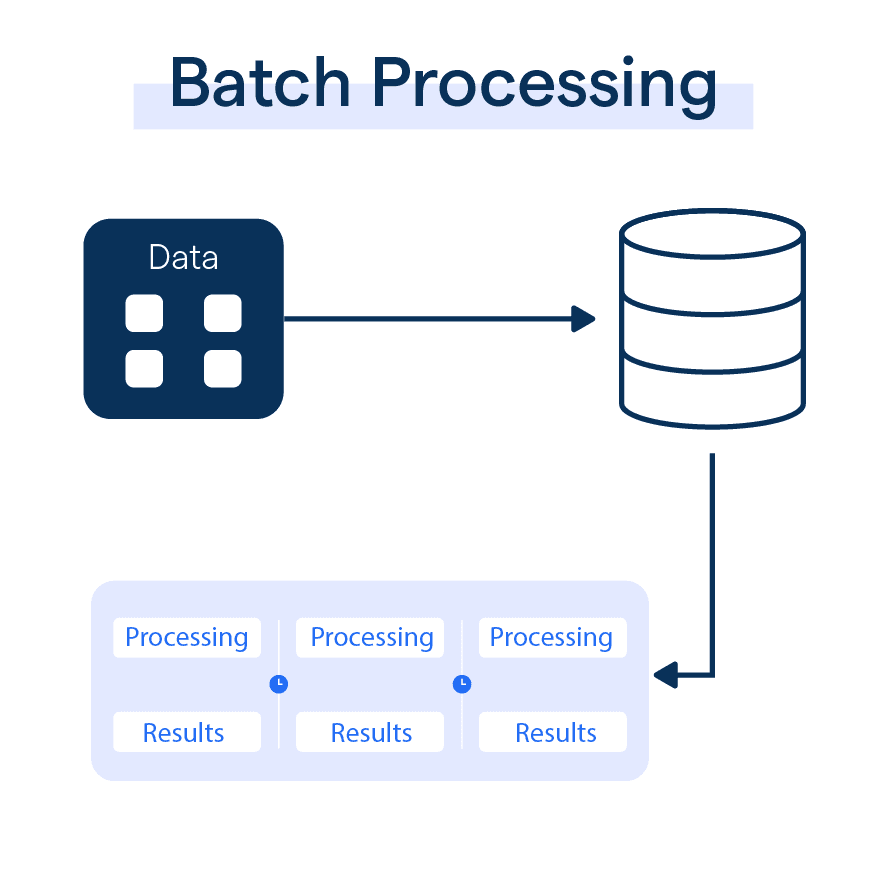
Batch processing executes automated routines across groups of files without requiring manual operator intervention for each individual item. Within intelligence and forensic environments, this approach applies to documents and data archives secured by government-approved cryptographic standards.
Manual decryption procedures fail when agencies handle thousands of protected records daily. Automating the workflow ensures that encrypted files move through validation, key matching, and decryption stages continuously.
Core Architectural Components
A reliable batch decryption infrastructure relies on several distinct functional layers:
- Ingestion directories configured to isolate encrypted files awaiting cryptographic review.
- Secure authentication modules that validate operator permissions before initiating batch jobs.
- Algorithm selection engines that identify encryption ciphers automatically based on file headers.
- Output repositories secured with restricted access controls for successfully processed plaintext data.
- Immutable logging services that record system actions for auditing and compliance verification.
Technical Implementation Strategies
Designing a robust automated decryption system requires selecting appropriate development frameworks and integration patterns. Engineering teams often build custom pipelines using scripting languages or deploy enterprise-grade platforms depending on throughput requirements.
Script-Based Workflows
Many technical units implement custom automation using Python or PowerShell to maintain precise control over execution steps. A well-constructed script performs several sequential checks:
- Traverse designated directory structures to discover encrypted files while validating file integrity hashes.
- Query secure key vaults or Hardware Security Modules to retrieve authorized decryption keys.
- Apply the appropriate cryptographic algorithm to process files in controlled batches.
- Verify output readability and move processed files to encrypted destination directories.
- Generate structured audit logs detailing success states and error codes.
Enterprise Security Integration
Large-scale operations often integrate specialized commercial decryption platforms with existing identity management systems. These platforms provide centralized control panels, role-based access restrictions, and automated threat detection mechanisms to flag abnormal decryption requests.
Legitimate Use Cases and Applications
Automated decryption pipelines serve critical operational functions across national security, law enforcement, and enterprise data management.
Digital Forensics Investigations
Investigators seizing storage media during cybercrime investigations frequently encounter diverse encryption schemes. Batch processing enables forensic examiners to analyze multiple hard drives and container files concurrently, reducing the time needed to surface actionable evidence.
Intelligence Analysis Pipelines
Agencies ingest encrypted communications from various authorized channels. Automated systems allow analysts to decrypt and categorize intercepted or shared data swiftly, ensuring time-sensitive intelligence reaches decision-makers without delay.
Infrastructure Migration Projects
When organizations transition to upgraded storage architectures or migrate classified archives to new cryptographic standards, batch processing facilitates large-scale re-encryption cycles with minimal downtime.
Security Considerations and Best Practices
Deploying high-speed decryption capabilities introduces inherent risks. Organizations must enforce multi-layered security controls to prevent unauthorized access or insider threats.
Access Control and Authentication
Rigorous authentication safeguards ensure only authorized personnel can trigger decryption routines. Implementing multi-factor authentication, strict role-based permissions, and a formal separation of duties between operators and approvers prevents unauthorized data exposure.
Audit Trails and Logging
Comprehensive monitoring systems must capture precise timestamps, operator identifiers, file access paths, and specific keys utilized during every operation. Regular audit reviews help security teams detect anomalies or potential policy violations immediately.
Frequently Asked Questions
What encryption standards are typically handled by batch decryption systems?
Batch systems commonly process files secured under government-approved cryptographic protocols, such as AES-256 and legacy standards mandated by national security frameworks.
How do automated workflows handle corrupted or unrecognized files?
Robust scripts include exception-handling routines that isolate corrupted files into quarantine directories and log specific error codes without halting the entire batch queue.
Can batch decryption tools operate offline?
Yes. High-security intelligence environments require air-gapped systems where decryption tools operate entirely isolated from public networks, utilizing local secure key storage.
What role does artificial intelligence play in modern decryption pipelines?
Machine learning models assist by analyzing file headers to predict optimal decryption sequences and flagging unusual access patterns that suggest compromise.



