Navigating modern enterprise environments requires a dependable gateway to verify user identity and protect sensitive assets. An authentication portal serves as the single entry point for users to verify their credentials before gaining entry to restricted systems, internal networks, or cloud applications.
Understanding how these portals operate helps users avoid common login pitfalls while maintaining rigorous security standards. Whether you're accessing corporate assets or administrative dashboards, knowing the mechanics behind secure access ensures smooth daily workflows without compromising data safety.
Core Architecture of an Authentication Portal
At its foundation, an authentication portal acts as a digital bouncer. It intercepts incoming connection requests and demands proof of identity before letting traffic pass into protected networks.
Most portals rely on centralized identity providers. Instead of maintaining separate passwords for every distinct application, users enter a single set of master credentials. The portal then issues a cryptographically signed token that downstream services trust.
- Credential Capture: The interface collects user identifiers and passwords over encrypted channels.
- Identity Verification: Backend directories check the submitted data against hashed and salted records in a secure database.
- Token Issuance: Upon successful validation, the system generates a session token, establishing temporary authorized access.
Step-by-Step Access Protocol
Gaining entry through an official login gateway involves a precise sequence of events. Skipping steps or ignoring browser warnings often leads to failed connection attempts or security flags.
- Verify the URL: Check the browser address bar to ensure you're visiting the official portal domain rather than a deceptive phishing replica.
- Input Primary Credentials: Type your assigned username and password carefully, watching out for unintended character shifts or caps lock errors.
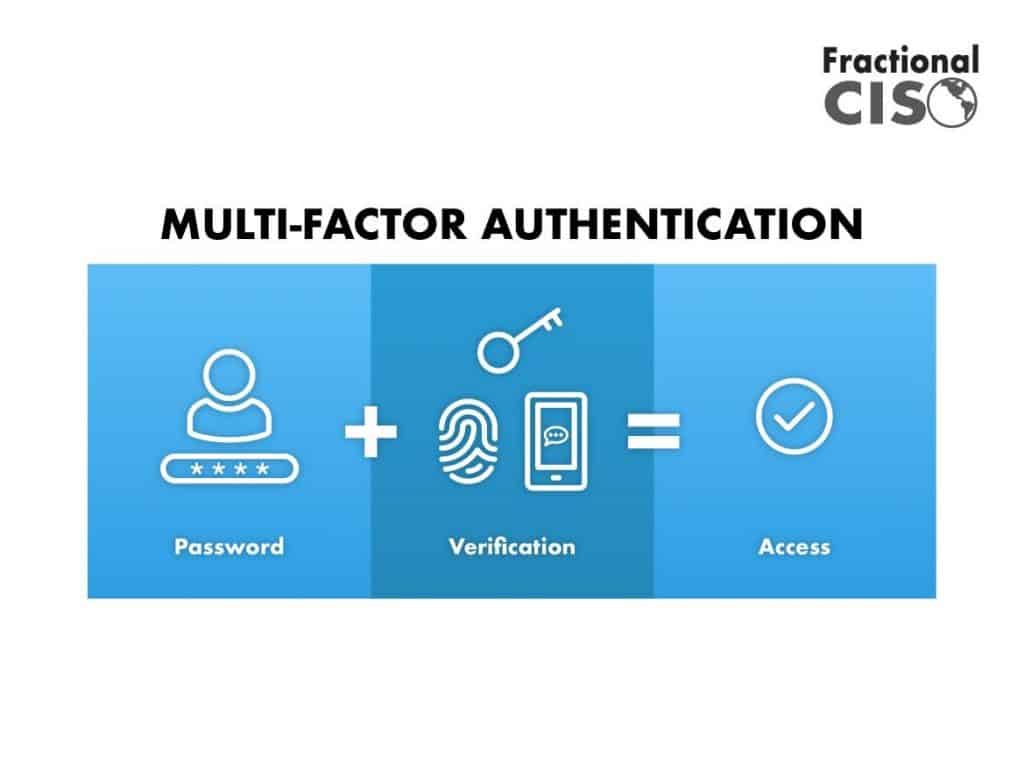
- Complete Secondary Verification: Provide your multi-factor authentication token, such as an authenticator app code or hardware key prompt.
- Establish the Session: Once the dashboard loads, your encrypted session token maintains your authenticated state while you navigate permitted resources.
For official standards on digital identity guidelines, refer to the National Institute of Standards and Technology.
Essential Security Protocols
Protecting access gateways demands more than a basic password policy. Modern portals incorporate multiple layers of defense to mitigate credential stuffing and interception risks.
Multi-Factor Authentication Requirements
Passwords alone can't stop automated credential attacks. Requiring a second factor—such as a time-based one-time password or biometric confirmation—stops unauthorized intruders even if your primary password leaks.
Transport Layer Encryption
All data transmitted between your browser and the portal server must use modern Transport Layer Security protocols. This encryption ensures that interceptors cannot read passwords or session tokens in transit.
Common Login Obstacles and Fixes
Even well-designed portals throw errors when edge cases occur. Knowing how to diagnose these issues saves time and reduces helpdesk ticket volume.
- Account Lockouts: Entering incorrect passwords past the threshold triggers automatic lockouts. Contact your system administrator to clear the security block.
- Browser Incompatibility: Outdated web browsers often fail to execute modern cryptographic scripts required by secure portals. Keep your software updated to the latest stable release.
- Session Timeouts: Inactive sessions expire automatically to prevent unauthorized physical access. Refresh your credentials if your session drops unexpectedly.
To review broader security operations frameworks, consult the Cybersecurity and Infrastructure Security Agency.
Frequently Asked Questions
What should I do if I suspect my portal credentials are compromised?
Immediately notify your IT security team or system administrator to revoke active session tokens and freeze account access. Change your password immediately from a trusted, secure device if access remains possible.
Why does the portal require multi-factor authentication every time?
Some environments configure strict session policies that suppress trusted device memory for high-security areas. This ensures that even if you walk away from an unlocked computer, unauthorized users cannot access restricted modules.
Can I save my portal password in a browser extension?
While browser password managers offer convenience, enterprise environments often recommend dedicated vault applications that encrypt credentials locally and integrate directly with single sign-on protocols.
What causes a generic authentication error message?
Portals intentionally display vague error messages—such as invalid credentials—to prevent attackers from learning whether a specific username exists in the system directory. Always double-check your spelling and caps lock status.



